EnergyPortal
Identity and roles, tenant boundaries, audit trails, data access, backup and deployment governance.
Security and Trust
Review Enlogy security principles for EnergyPortal, enPowerManager, enCoreEnergy, Scadify, remote access, roles, audit trails, backups, updates and industrial edge operation.
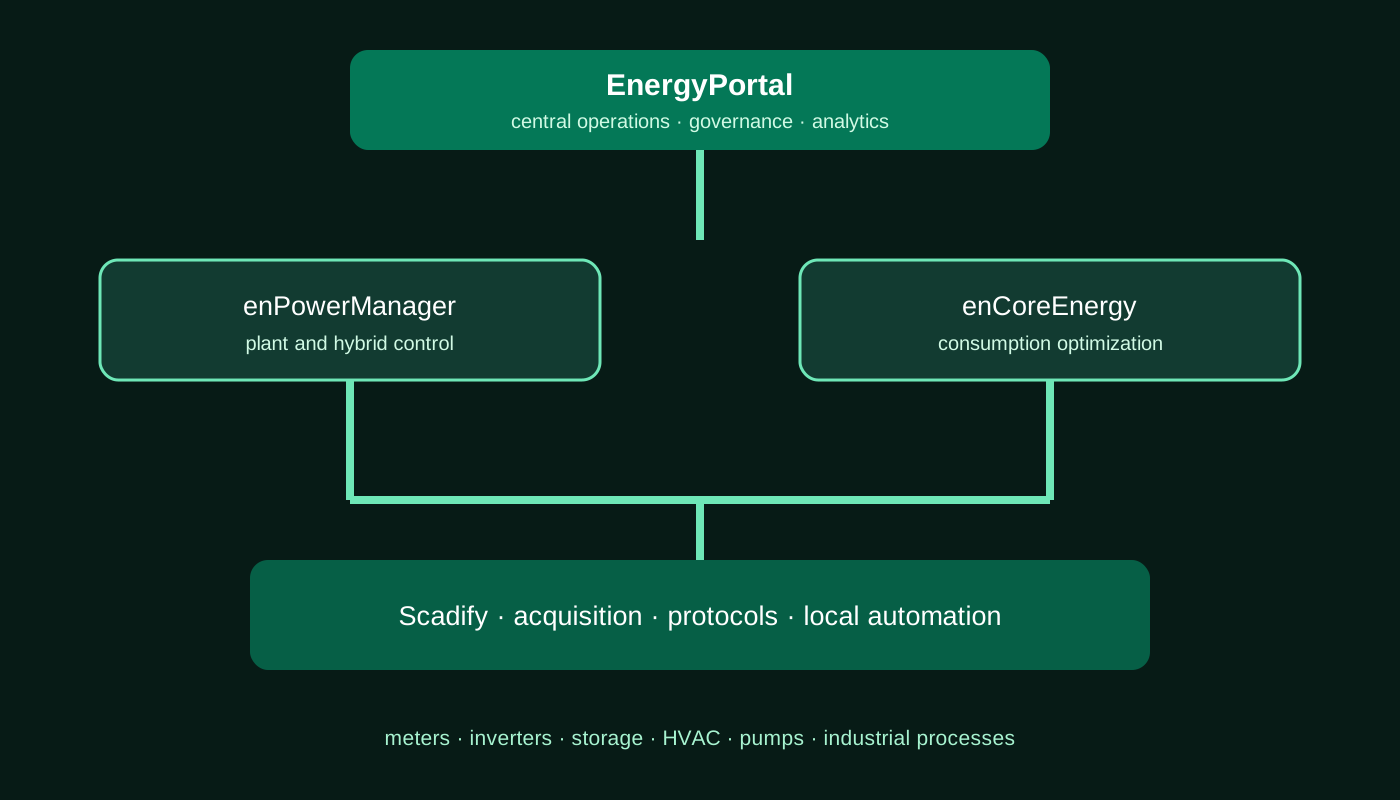
Identity and roles, tenant boundaries, audit trails, data access, backup and deployment governance.
Controlled command paths, setpoint traceability, fail-safe design and project-specific interfaces.
Role-based workflows, human approval, multi-site governance and audit history.
Local-first operation, device identity, configuration management, updates, rollback and offline resilience.
| Standard | Status |
|---|---|
| ISO 27001 | Not claimed |
| IEC 62443 | Not claimed |
| NIS2 / NERC CIP | Not claimed |
Controls depend on product release, deployment model, network architecture, customer policy and project engineering. This page does not create a certification, compliance or availability claim.
Standards compliance for this capability
Enlogy provides full compliance with the standards below across development, integration and system operation and management.
IEC 62443 · IEC 62351 · ISO/IEC 27001 · ISO/IEC 27002 · ISO/IEC 27019 · NIST SP 800-82 · NIST CSF 2.0
Connected energy systems need controlled access, secure communication and a manageable cyber-risk lifecycle.
Enlogy applies industrial and energy-sector security across development, identity, OT interfaces, communication, monitoring and incident workflows.
Explore this capability: IEC 62443 OT cybersecurityWe use necessary storage to remember your choice. With your permission, Google Analytics measures visits and interactions; advertising options allow Google advertising measurement and optional personalised advertising. You can reject optional cookies and keep using the site.
Your choice is stored in this browser for up to 180 days. Change it at any time using Cookie preferences. Contact info@enlogy.com with privacy questions.